Edge-to-Edge
Direct site-to-site connectivity.
ACURIX SD-WAN · ACURIX EDGE LICENCE UPGRADE
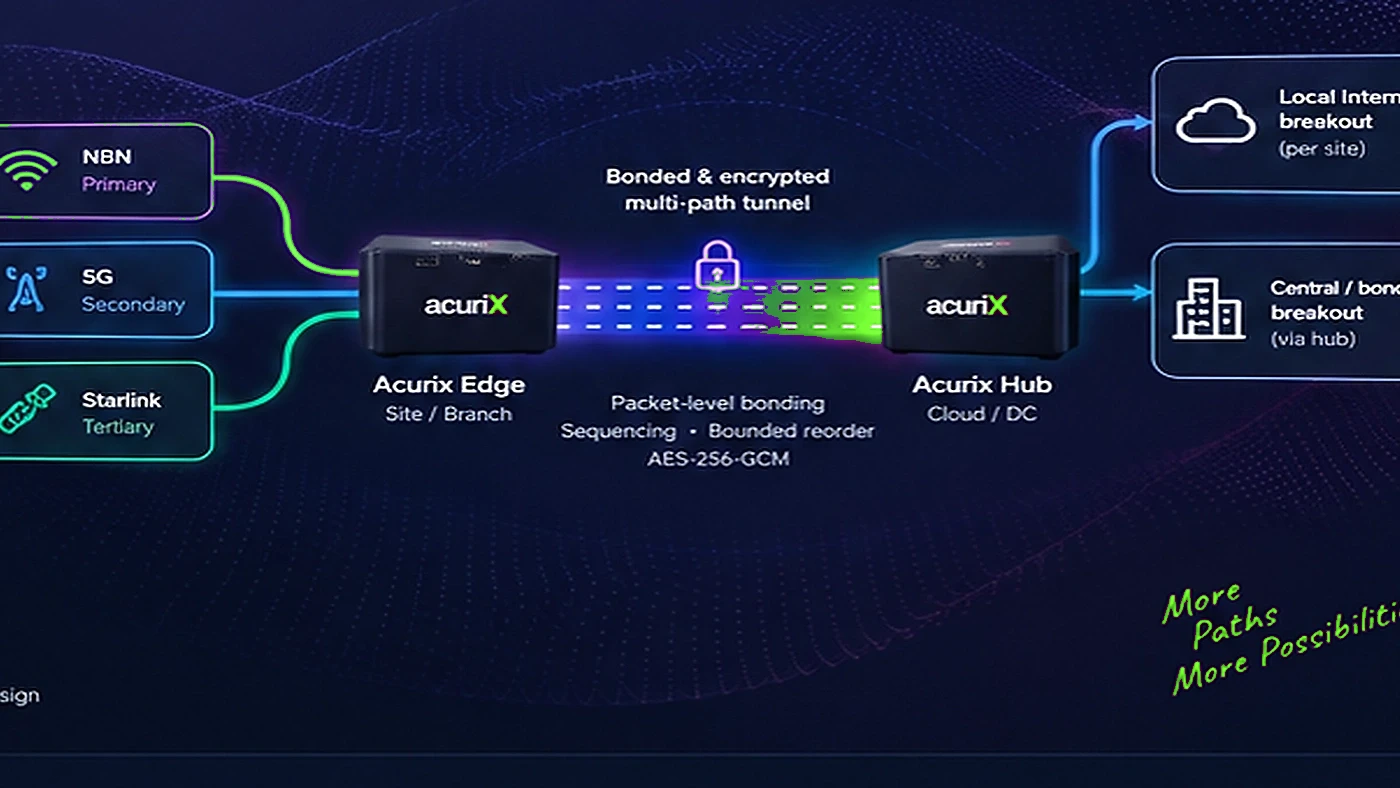
Packet-level multi-WAN bonding, adaptive path selection and resilient branch connectivity. Activate Acurix SD-WAN on the same Acurix Edge device and Edge OS.
OVERVIEW
Direct site-to-site connectivity.
Connect remote sites to a central hub.
Bonded links between data centres.
Many sites, one hub.
Simple, dedicated connections.
Connect sites on demand.
CAPABILITIES
Send packets across all healthy links.
Balance by link quality, capacity or policy.
Duplicate critical traffic for extra reliability.
Route by application, user or destination.
Automatic failover when links degrade.
Forward error correction for high-loss links.
DEPLOYMENT
Acurix uses one security model across Edge and Hub. Firewall policy, breakout location, NAT and SD-WAN treatment are evaluated together so a routing decision cannot silently bypass security.
Stateful policy, zones, address/service objects, NAT, anti-spoofing, connection tracking and structured logging.
Local, Metro/Hub and customer-central breakout can coexist. Every Internet path crosses the appropriate firewall.
Service chains allow a supported FortiGate or other VNF at the Hub or future Edge NFV tier. Existing physical firewalls can also remain in-path.
Included with Edge and Hub. Designed for branch segmentation, NAT, stateful Internet protection and SD-WAN-aware policy.
For customers standardised on an enterprise NGFW, Acurix can retain SD-WAN while inserting the customer's chosen firewall platform.
USE CASES
A clear view of your links, performance and network health — all in one place.
OPERATIONS
v0.1.0-alpha1 remains the tested SD-WAN baseline. Native firewall, breakout security and service-chain support are the approved v0.2.0-alpha1 implementation target and are not yet claimed as built or qualified.
NEXT STEPS
Acurix SD-WAN is a standalone product, and may integrate with Acurix Gateway, Acurix Splash and Managed Services.
LET’S TALK