Retail & Hospitality
Keep stores and venues connected with resilient Internet and secure access.
ACURIX EDGE
Secure site routing and resilient branch connectivity. Optional SD-WAN licence upgrade on the same Edge OS and device.
OVERVIEW
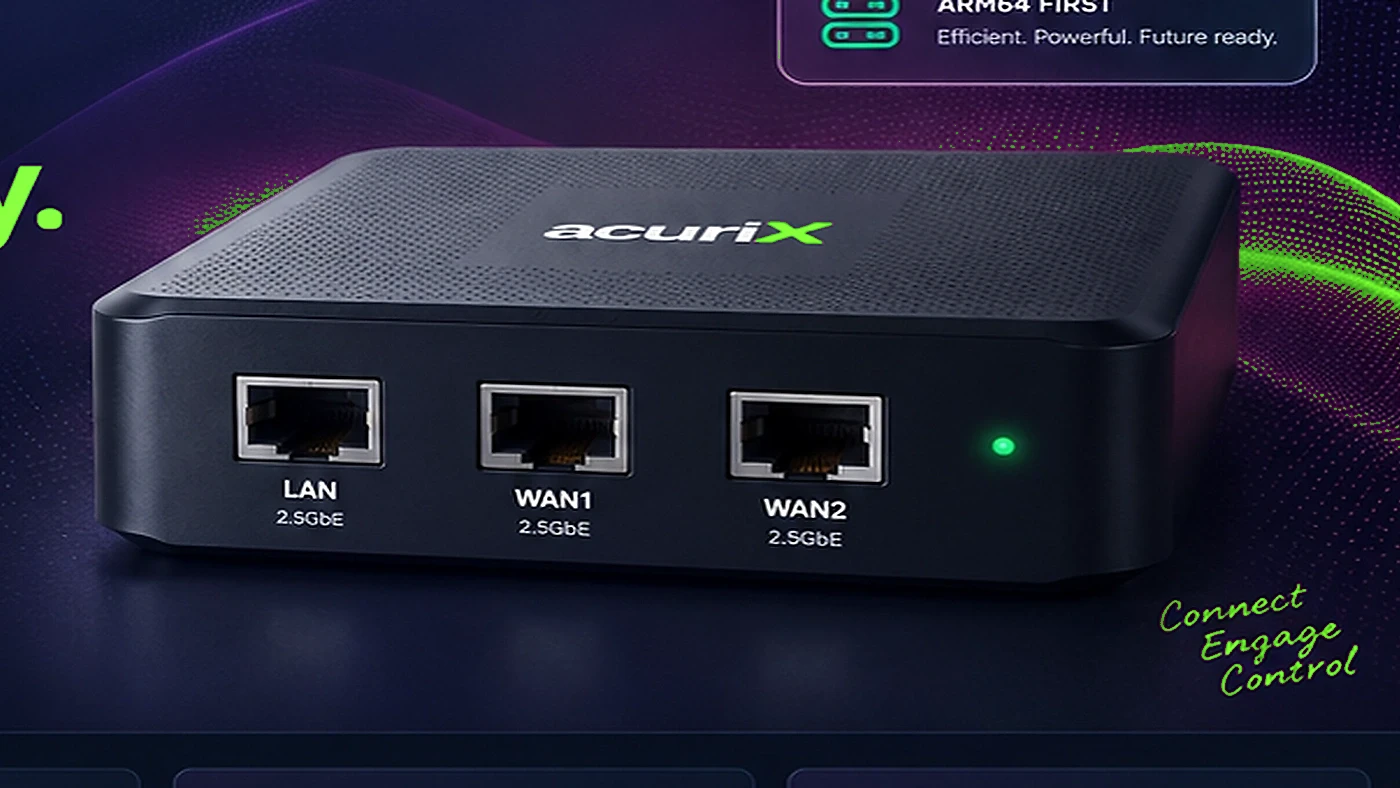
Acurix Edge keeps people, sites and devices connected with secure, resilient multi-WAN connectivity. Ideal for regional sites, retail, education, healthcare, construction and remote locations.
Keep stores and venues connected with resilient Internet and secure access.
Reliable connectivity for schools and campuses, even in regional areas.
Secure, always-on connectivity for clinics and care facilities.
Stay connected on site and in remote locations with flexible WAN options.
CAPABILITIES
The standard Edge does not require a third-party firewall VM. Acurix policy is compiled to Linux nftables and conntrack for stateful enforcement while preserving the SD-WAN fast path.
Corporate, Guest, IoT, Voice, SD-WAN, Internet and Management zones with explicit allow/deny policy.
WAN access to WebUI and SSH is denied by default; only authorised management paths are exposed.
Local Internet traffic traverses the Edge firewall and NAT before WAN egress. No local bypass around policy.
Corporate traffic can be firewall checked at Edge, bonded to the Hub, checked again centrally and NATed from a stable public egress.
DEPLOYMENT
Deploy Acurix Edge at a single site, or as part of a national rollout. Centrally manage and monitor with Acurix, and integrate with your existing infrastructure.
USE CASES
Multi-WAN bonding and failover Keep traffic moving, even when links fail.
Native Acurix Firewall Stateful zone security, segmentation and NAT in the Linux kernel fast path.
Target 2 Gbps bonded throughput Approximately 2 Gbps useful encrypted bonded throughput on the standard Edge, subject to physical testing.
OPERATIONS
LET’S TALK